

As WordPress continues to grow in popularity, so does the complexity of this open source CMS. WordPress has come a long way from its early days in 2003 as a basic blogging platform and has become the most popular online publishing platform in the world.
Your website is a valuable business resource, and just like in real life there are individuals out there who want to take advantage of opportunities to benefit at the expense of others. If you own a website built in WordPress, then you know the ease and accessibility the open source CMS offers. However, the continued additions to WordPress can leave ways that hackers can use to access your website without your authorization.
The API Rest Vulnerability Found In The Wild
This WordPress 4.7 exploit was discovered on January 20, 2017, by WordPress security firm Sucuri. Marc-Alexandre Montpas, a security analyst at Sucuri, was the first to find the vulnerability during routine checks of open source projects. After discovering this vulnerability, Montpas promptly notified the WordPress security team and passed along his findings.
After being notified, WordPress contacted various companies to help protect users while they developed a fix for the REST (Representational State Transfer) API vulnerability. The WordPress security team worked diligently to create a fix for this vulnerability, and within only six days WordPress released a patch in version 4.7.2 on January 26, 2017. The details were disclosed to the public on February 1, 2017.
If your WordPress website has been hacked, we can help with our WordPress malware removal service, where we clean and update your site, usually within 24 hours. We also offer a 30-day period of free cleaning in case your WordPress website gets hacked again.
How Does A Hacker Exploit the REST API Vulnerability?
The WordPress REST API content endpoints were added to the core code of WordPress and enabled by default in version 4.7.0. The bug affected only WordPress 4.7.0 and 4.7.1. This API allows different computer programs to access your website to update, create, and delete WordPress posts. For example, if your website wants to display specific content based on the location of your visitor, then the REST API makes it easy to show this dynamic content.
Since the REST API looks for individually crafted HTTP requests to specific URLs, anyone can send a request to the public API URL of any website. Through some basic manipulation of that request, anyone could edit the posts on an unpatched site without logging in.
If someone knows how to fool the gatekeeper that WordPress uses to discern user credentials, then they will be able to alter content on your website.
Think your site has been hacked? We remove the malware, close the hole it came through and lock the site down for a flat $249. See malware removal →
What’s The Risk Of This Exploit For Your Business?
Within a week of the vulnerability going public, thousands of WordPress websites had fallen victim to several malicious groups. Some of these groups alter content on vulnerable sites as a way to brag about their abilities, but others take advantage of the vulnerability to benefit their interests. The main types of exploits hackers used in the wild were defacement campaigns, SEO spam and crimeware injections.
Defacement Campaigns
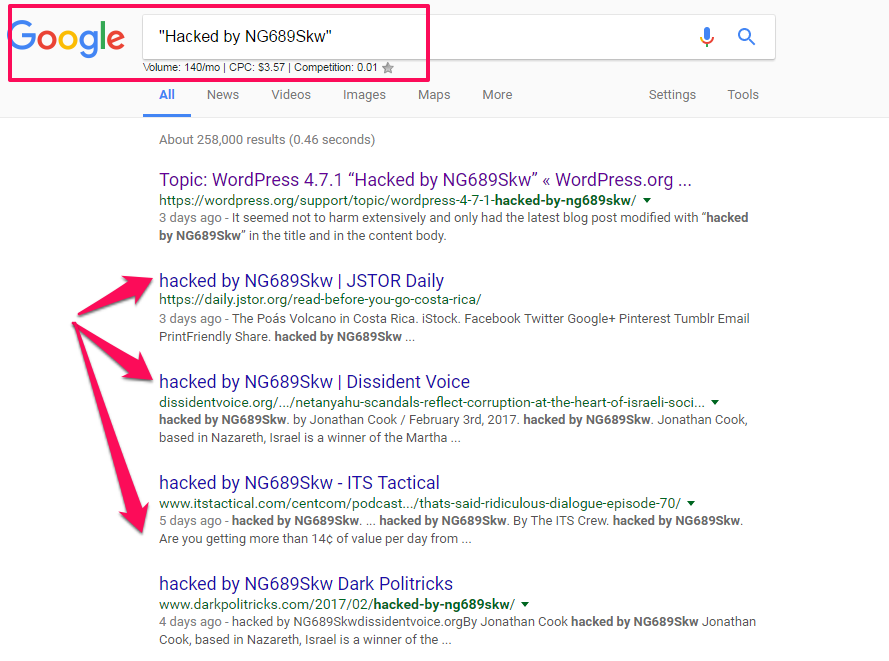
Some hacking groups used this vulnerability to deface company websites, usually by replacing post titles and content with a “Hacked by” message followed by the group’s name. While not irreversible or a business-ending hack, victims will find their SERPs displaying headlines and other content displaying different information than intended. If your website is hijacked and falls victim to this exploit, then you will be showcasing messages not approved by your brand.
Defacement campaigns are some of the easiest attacks hackers can perform on a vulnerable website. Just by changing the titles and meta information of your pages, they can change how your site appears in search results.
SEO Spam Exploitations
Defacement campaigns are not the only way hackers are exploiting the vulnerability. Savvy attacks also include manipulating site content to serve the SEO interests of unauthorized users.
Also known as “spamdexing”, SEO Spam is the practice of creating websites or online content that will rank high in search engines through illegitimate strategies.
Since the REST API vulnerability allows hackers to access vulnerable sites, malicious groups have the ability to inject new content into pages and images on your website. This new, unapproved content could not only serve their interests, but this type of attack will also hurt your brand.
While defacing campaigns could hurt your online reputation, SEO spam exploitation could become the prominent way that hackers abuse the vulnerability for monetary interests. The reason SEO spam will be the most popular exploit is that hackers can use vulnerable websites to boost their online rankings with backlinks and other SEO practices.
Other Content Injection Attacks
While having your SERPs altered or SEO spam could hurt your business, there are other more severe content injection attacks that hackers can perform on your site using this vulnerability. The most concerning content injection attack that a hacker could perform on your website is placing code on your site that would cause your visitors to download harmful content.
Once a hacker gains access to your website using the REST API vulnerability, they could add malicious content to your pages. In some instances, this content can install crimeware on a user’s computer by using pre-existing web browser vulnerabilities.
After this code runs on a computer, the user could be asked to download and install software that contains malicious programs. This means that if your website is not updated, a hacker can use your site as a tool to harm your visitors all without your knowledge.
Protecting Your WordPress Website
We suggest that site owners take basic precautions to protect their site. The first defacement campaigns were seen within 24 hours of the vulnerability being made public, and the number of attacks grew quickly after that. So, what should you do if you find yourself a victim of these malicious attacks?
- Make a complete backup of your database and files for your website. Move these files to a safe location, so you always have something to reference moving forward.
- Update WordPress to 4.7.2 or later (today, the latest version).
- Locate and restore the most recent backup files you have before the attack.
- Log in to /wp-admin/ and check that WordPress, your theme and your plugins are on their current versions.
- Audit your website to ensure that all files are clean of the exploit and your content is as it was before the hack.
- Consider using cloud-based web application firewalls (WAF) to prevent these types of attacks in the future.
The most efficient solution to protect your WordPress site is also the easiest. The best way to harden your WordPress installation is to keep your WordPress version and plugins updated at all times. For more ways to keep your WordPress site from getting hacked, see our guide.
We know that restoring a compromised website is never easy and requires a great deal of careful work. I am so pleased I chose FixMyWP.com, their communication was prompt and the service was extremely thorough and professional.
What To Do If Your WordPress Website Is Hacked
Keeping your site and plugins updated can take a lot of time and energy, and sometimes you can easily forget to update your website. Unfortunately, there are individuals out there who will exploit your business for their gains. The REST API vulnerability showed how easy it is for unauthorized users to take advantage of honest, hardworking business owners like yourself.
It can be overwhelming and stressful if your website is hacked. No one likes the feeling of being a victim, and you have worked too hard to let dishonest people profit from it. Instead of worrying about the technical side of things, you can trust the years and experience of FixMyWP to clean your WordPress and get your business back on track.
Think your site has been hacked?
We remove the malware, close the hole it came through and lock the site down. Flat rate of $249, usually done the same day or within 24 business hours.